Identify the exposure
Examine the data being accessed, the destination and the identity behind the request.
 AckuityRequest access
PLATFORM CAPABILITY / DATA PROTECTION FOR AI AGENTS
An agent can retrieve the right information and still send it to the wrong place. Connect data policies to the user, task and destination before information leaves its permitted scope.
Early access. Already in paid production.
Summarize support trends for the product team.
The task needs aggregate trends. The export contains customer email addresses.
A PLAUSIBLE ACTION. A MATERIAL RISK.
The proposed destination and data exceed the authorized task.
Try a context challengeThe task needs aggregate trends. The export contains customer email addresses.
BlockFROM VISIBILITY TO CONTROL
Examine the data being accessed, the destination and the identity behind the request.
Use data rules and execution context to evaluate sensitive fields and permitted use.
Apply configured controls at the integrated boundary. A permitted alternative could use an approved tool and an aggregate dataset.
INSIDE ACKUITY
The Data Rules screen exposes field-level alert and masking settings. The scenario above is illustrative.
See it with your team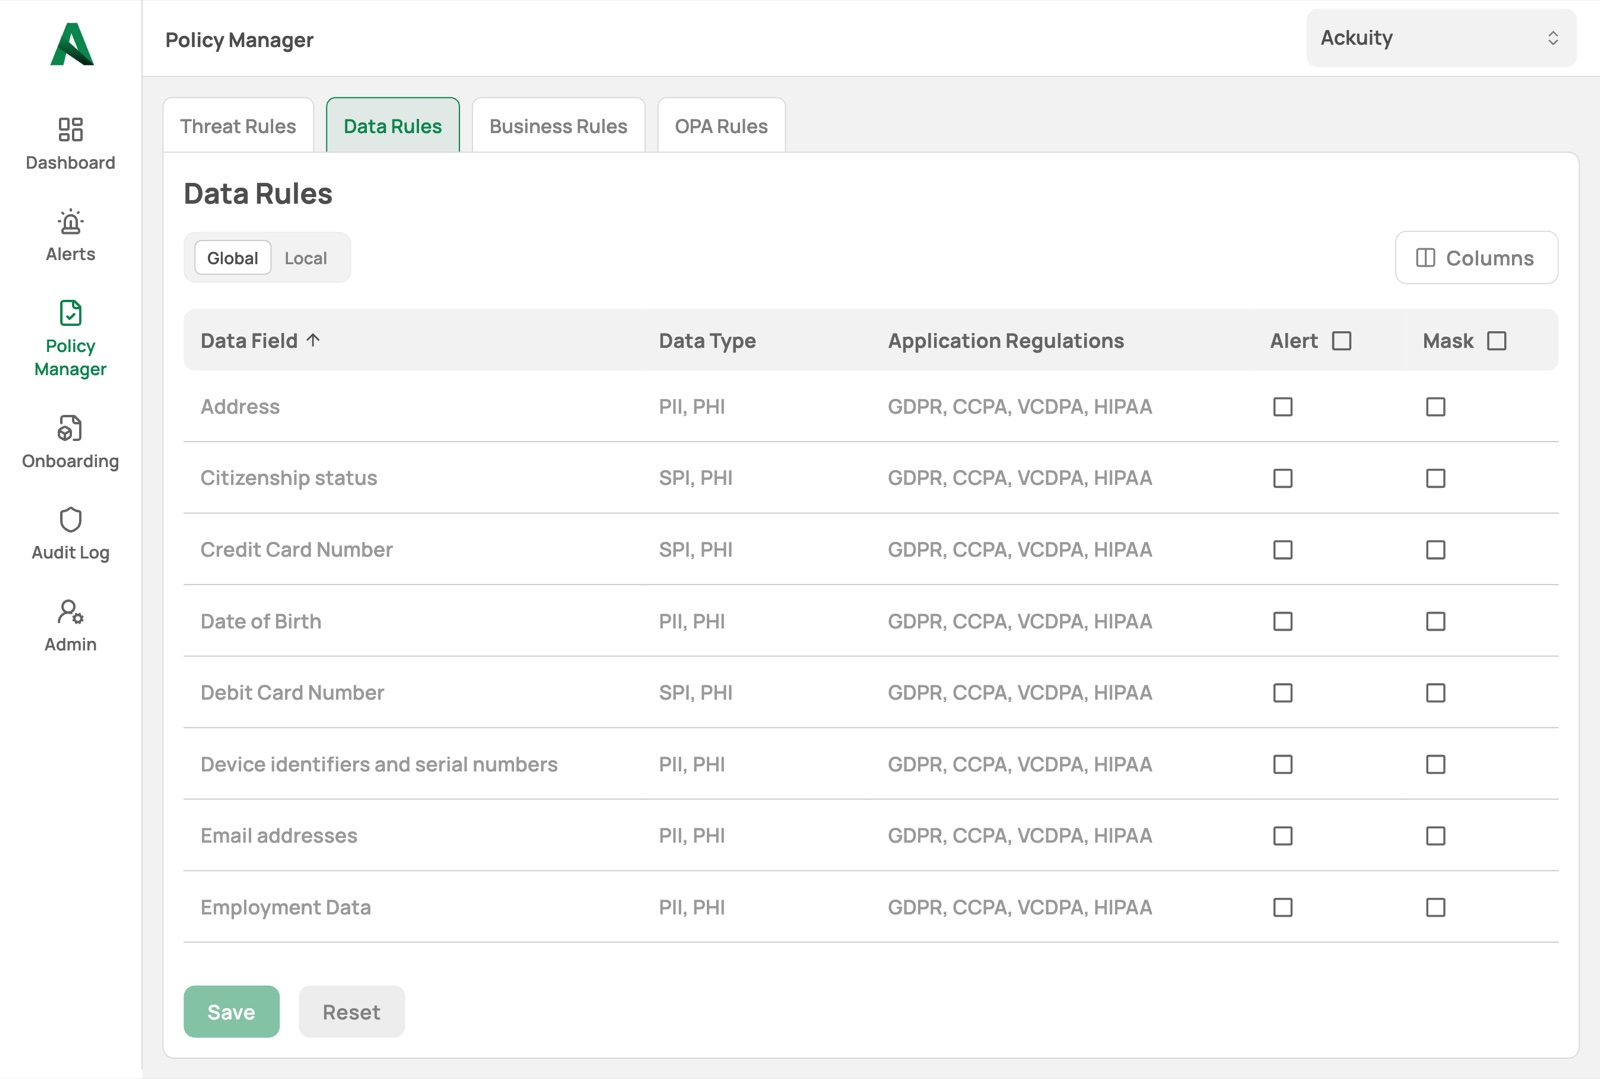
YOUR QUESTIONS, ANSWERED
Prompt filtering inspects inputs or responses. Agent data protection also considers retrievals, tool arguments, recipients and destinations across the execution flow.
No. Tokenization can reduce exposure of sensitive values, but access, purpose and destination still matter. Confirm the available transformations and integration points for your environment during a walkthrough.
No. Technical controls support your security program. Their suitability depends on the data, configuration, processes and regulatory obligations involved.
CONTINUE YOUR REVIEW
NEXT STEP
Review your environment and the controls your team needs. Begin with read-only discovery.